 EN
 Deutsch
 Español
 Français
 Italiano
 Português
 Nederlands
 Polski
 Bahasa Indonesia
 Русский
 Українська
 العربية
 עברית
 हिन्दी
 日本語
 한국어
2025-12-04
Turn Microsoft Threat Analytics into Real Security Action
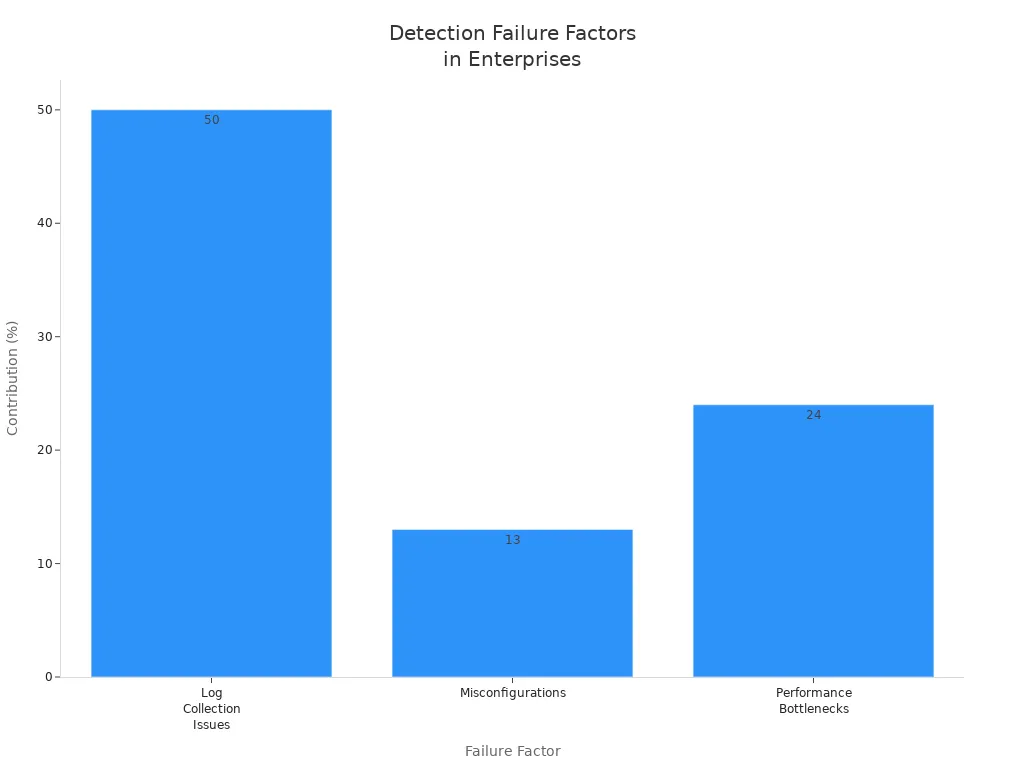
Are you frustrated with your threat analytics? You’re not alone. Three in four organizations, or 75%, report dissatisfaction with their current ability to detect and investigate threats. Many face a significant gap between data collection and actionable security improvements.
Consider these questions: Are you truly leveraging your threat analytics? What insights have you turned into effective actions? If you can't answer these, your threat analytics is useless, leaving your organization vulnerable.
Key Takeaways
- Assess your threat analytics regularly to ensure they lead to actionable insights.
- Act on threat data promptly to avoid financial losses and security breaches.
- Integrate real-time threat intelligence to enhance detection and response times.
- Utilize threat hunting to proactively identify risks before they escalate.
- Break down data silos to improve collaboration and comprehensive threat analysis.
- Implement user behavior analytics to detect insider threats early.
- Adopt continuous monitoring to adapt to the evolving threat landscape.
- Measure and communicate the effectiveness of your threat intelligence efforts.
Why Threat Analytics Is Useless Without Action
The Actionability Gap
Many organizations collect vast amounts of threat analytics data, yet they struggle to translate this information into effective security measures. This gap between data collection and actionable insights can create a false sense of security. You might feel confident in your analytics capabilities, but without taking action, your organization remains vulnerable to security breaches.
Consider the measurable consequences of failing to act on threat analytics findings:
| Consequence | Description |
|---|---|
| Financial Liability | Unmeasured human risk can lead to significant financial losses due to security breaches. |
| Lack of Clear Metrics | Without metrics, organizations cannot identify potential risks or prevent incidents effectively. |
| Increased Training Time | Proactive measures can reduce training time by up to 40%, indicating inefficiencies without action. |
These consequences highlight the importance of not just collecting data but also acting on it. Security teams must prioritize turning insights into defensive actions to enhance their cybersecurity posture.
Turning Insights Into Defense
To effectively utilize threat analytics, you need a structured approach. This involves integrating findings into your security operations. Here are some effective processes for turning threat analytics insights into actionable defense:
| Update Aspect | Description |
|---|---|
| Upgraded Detections | Enhancements to detection capabilities improve the actionability of threat insights. |
| New Analytic Format | A format that aligns with everyday defender tools like SIEMs and Sensors for better integration. |
| Cross-Domain Insights | Insights that span multiple domains provide a comprehensive view of adversary tactics. |
By implementing these updates, you can transform your threat analytics from passive reports into active defense mechanisms. This proactive approach not only improves detection but also reduces dwell time, allowing your security teams to respond swiftly to potential threats.
The Role of Real-Time Threat Intelligence
Risks of Outdated Data
Relying on outdated threat intelligence can expose your organization to significant risks. When you depend on old data, you may miss critical threats that could compromise your security. Here are some key risks associated with outdated threat intelligence:
| Risk Description | Explanation |
|---|---|
| Missing real-time threats | Organizations may overlook current threats due to reliance on outdated data. |
| False sense of security | Having outdated intel can lead to complacency, as teams believe they are protected. |
| Ineffective security tools | Security systems may fail to respond to new threats if they are only fed old data. |
These risks highlight the importance of maintaining up-to-date threat intelligence. Without it, your organization may remain blind to emerging threats, leaving you vulnerable to attacks.
Benefits of Real-Time Updates
Implementing real-time threat intelligence significantly enhances your cybersecurity posture. By leveraging current data, you can proactively defend against cyber attacks. Real-time updates allow you to reduce the mean time to detect (MTTD) from days to minutes. This swift detection capability enables you to respond quickly, minimizing the impact of potential breaches.
Organizations that utilize real-time threat intelligence can achieve a reduction of up to 27% in the average time required to detect and contain a breach. This improvement not only lessens the potential damage from cyberattacks but also transforms your threat response from a passive approach to an active one.
Moreover, real-time threat intelligence allows security analysts to make informed decisions quickly. For instance, non-MDR clients spent an average of 19 hours per incident for Business Email Compromise (BEC), while MDR clients reduced this time to just 2 hours. This nearly 90% decrease in time to resolution demonstrates the effectiveness of real-time updates in enhancing your security operations.
By integrating real-time threat intelligence into your cybersecurity strategy, you can stay ahead of threats and significantly improve your overall security posture.
Enhancing Cybersecurity With Threat Hunting
What Is Threat Hunting?
Threat hunting is a proactive approach in cybersecurity. It involves searching for potential threats before they trigger alerts. This method relies on human analysts who manually investigate data and form hypotheses. Automated tools support these analysts, enhancing their ability to detect hidden threats. The goal is to identify risks early, preventing significant harm like data breaches or ransomware attacks.
Here’s a breakdown of key elements of threat hunting:
| Element | Description |
|---|---|
| Proactive, not reactive | Threat hunting focuses on finding issues rather than waiting for alerts. |
| Manual investigation | Analysts examine data and form hypotheses, supported by automated tools. |
| Early detection | The aim is to identify threats before they can cause significant harm. |
Integrating Threat Hunting and Analytics
Integrating threat hunting with your existing threat analytics can significantly enhance your cybersecurity posture. This combination allows you to detect advanced persistent threats more effectively. Here are some benefits of this integration:
- Centralizing data from networks, applications, and security systems in a SIEM platform enhances your ability to detect long-term trends.
- Understanding the context of threat actor techniques is crucial for identifying evidence of their activities.
- The threat hunting process involves preparing baselines, developing hypotheses, executing hunts, validating results, and receiving feedback to improve future hunts.
To achieve effective threat hunting, you need to focus on several key areas:
- Identify critical assets and sensitive data to focus your threat hunting efforts effectively.
- Understand the Tactics, Techniques, and Procedures (TTPs) of attackers to recognize unusual patterns.
- Establish a baseline of normal behavior to detect deviations that may indicate threats.
Organizations that successfully integrate threat hunting into their Security Operations Center (SOC) workflows report a 40% improvement in overall threat detection. Additionally, automation triggered by threat hunting can lead to a 78% reduction in incident response time. Collaboration across security teams enhances the overall security posture by sharing discoveries and coordinating with IT teams.
To implement effective threat hunting, your team should possess a mix of technical and analytical skills. These include:
- In-depth understanding of operating systems and networking.
- Strong data analysis capabilities to identify patterns.
- Certifications such as CISSP and CEH to demonstrate knowledge.
Moreover, having a natural curiosity and methodical analysis approach is essential for digging deep into data. By combining these skills with the right tools, you can create a robust threat hunting team that actively seeks out and mitigates risks.
Overcoming Poor Data Integration
Data Silos and Their Impact
Data silos can severely limit the effectiveness of your threat analytics. When data remains isolated within departments or systems, it creates barriers that hinder comprehensive analysis. You may miss critical insights that could enhance your security posture. Here are some common causes of data silos in cybersecurity environments:
| Cause | Description |
|---|---|
| IT strategy and technology deployments | Decentralized IT buying decisions lead to incompatible databases and applications, creating silos. The variety of data platforms also contributes to this issue. |
| Organizational structure and management | Silos often arise in decentralized business units, especially in large organizations with separate subsidiaries. |
| Corporate culture and principles | A lack of incentives for data sharing and a culture that views data as proprietary can foster the development of silos. |
| Business growth and acquisitions | Rapid growth and the creation of new business units can lead to silos, as can mergers and acquisitions that introduce hidden data silos into the organization. |
These factors can create blind spots in your threat detection capabilities. Without a unified view of your data, you risk overlooking potential threats that could compromise your organization.
Building Unified Data Streams
To overcome the challenges posed by data silos, you must focus on building unified data streams. This integration allows for a holistic view of your cybersecurity landscape. Unified data streams improve the accuracy and speed of threat analytics in several ways:
| Benefit | Description |
|---|---|
| Faster Onboarding | Databahn provides 500+ prebuilt connectors, reducing onboarding time from days to hours. |
| Simplified Data Normalization | Normalizes telemetry and maps fields to Sentinel's schema before data reaches the workspace. |
| Pre-ingestion Enrichment | Applies enrichment like geo-IP resolution and threat intelligence tagging before data lands in Sentinel. |
| Reduced Analytics Tier Ingest | Pre-ingestion volume filtering reduces analytics-tier ingest by 40–60%, improving cost-efficiency. |
Implementing these strategies can significantly enhance your threat analytics capabilities. Here are some best practices for building unified data streams in large organizations:
- Start with a targeted pilot project to gradually scale data management techniques, reducing risk and allowing for learning.
- Create a Central Data Platform to coordinate data activities across systems, enhancing management and security.
- Implement centralized governance and access restrictions early to ensure data integrity and compliance.
- Utilize automation for data quality management to improve accuracy and reduce operational costs.
- Employ data versioning to maintain historical data states, allowing for corrections when issues arise.
By integrating diverse data sources, you can create a more effective threat analytics framework. This approach not only enhances your detection capabilities but also fosters a culture of collaboration across your organization.
Improving Cyber Threat Detection
User Behavior Analytics
User Behavior Analytics (UBA) plays a crucial role in enhancing your cyber threat detection capabilities. By continuously monitoring user activities, UBA helps you identify potential insider threats early. Understanding that these threats often stem from human motives rather than just activities allows you to fuse various indicators of compromise. This holistic view aids in early detection and intervention, addressing potential threats before they escalate.
For instance, if an employee accesses sensitive information without proper authorization, UBA can flag this anomaly. By examining communication patterns, including tone and sentiment, you gain early insights into possible insider threats. This comprehensive analysis allows for a more informed response to emerging risks.
Adapting to Emerging Threats
The threat landscape is constantly evolving. Adaptive detection strategies are essential for responding to these emerging threats effectively. These threats often change tactics based on detection attempts. They may delay execution to avoid triggering alerts or mimic legitimate user activity to blend in.
To counter these adaptive threats, you should establish long-term behavioral baselines. Implement continuous monitoring instead of relying on snapshots. Utilize context-aware alerting to enhance detection. Visibility across networks, endpoints, users, and data flow is crucial. This visibility enables you to detect subtle behavior shifts and identify abnormal access patterns, which are essential for early containment before escalation.
Combining analytics, user behavior, and adaptive strategies significantly improves your threat detection rates. For example, AI systems can achieve a threat detection rate of 98%, while traditional systems may not provide comparable results. Anomaly detection identifies unusual network traffic or system behavior, while predictive modeling anticipates potential threats based on historical data.
By integrating these methods, you can enhance your detection coverage and improve your overall detection and response capabilities. This proactive approach not only helps you stay ahead of active threats but also fosters a culture of continuous improvement within your security operations.
In summary, your threat analytics might fail due to a lack of action, outdated data, and poor integration. To improve your cybersecurity posture, consider these recommendations:
- Regularly update threat data sources for timely identification of evolving threats.
- Automate threat detection and response to enhance speed and accuracy.
- Collaborate with threat intelligence communities for broader insights.
- Implement continuous monitoring to adapt to the changing threat landscape.
- Measure security performance to demonstrate the value of your threat intelligence efforts.
Reassess your threat analytics approach. Adopt proactive strategies like Breach and Attack Simulation (BAS) to identify gaps in your security controls. Leverage tools like Microsoft 365 Threat Analytics to transform your security operations and stay ahead of potential threats.
FAQ
What is threat analytics?
Threat analytics involves collecting and analyzing data to identify potential security threats. It helps organizations understand vulnerabilities and improve their defenses against cyber attacks.
Why is real-time threat intelligence important?
Real-time threat intelligence provides up-to-date information on emerging threats. It enables you to respond quickly, reducing the time it takes to detect and contain potential breaches.
How can I improve my threat detection capabilities?
You can enhance threat detection by integrating user behavior analytics, adopting real-time updates, and implementing proactive threat hunting strategies. These methods help identify threats before they escalate.
What are data silos, and why are they a problem?
Data silos occur when information remains isolated within departments. They hinder comprehensive analysis and can lead to missed insights, making your organization more vulnerable to threats.
How does threat hunting complement threat analytics?
Threat hunting proactively seeks out hidden threats before they trigger alerts. It enhances threat analytics by providing context and insights that improve detection and response capabilities.
What role does user behavior analytics play in cybersecurity?
User behavior analytics monitors user activities to identify anomalies. It helps detect insider threats early, allowing you to intervene before significant harm occurs.
How can I ensure my threat analytics are actionable?
To make threat analytics actionable, prioritize integrating insights into your security operations. Regularly update your data sources and establish clear processes for responding to identified threats.
What tools can help with threat analytics?
Tools like Microsoft 365 Threat Analytics provide powerful insights and recommendations. They help organizations detect and respond to threats effectively, transforming security operations from reactive to proactive.
🎧 Listen to this episode
Want a practical explanation of Turn Microsoft Threat Analytics into Real Security Action? This episode breaks down the topic in clear language and shows why it matters for Microsoft 365, Azure, Power Platform, security, AI, and modern work.
Listen to this episode if you want to:
- Understand the key concepts behind Turn Microsoft Threat Analytics into Real Security Action
- See how it fits into the wider Microsoft technology ecosystem
- Learn where it can create practical value for your organization
You may also enjoy these related M365 FM episodes:
- Real-Time Dynamics 365 Campaign Analytics in Fabric
- Dataverse Security - Simply Explained
- Azure Network Security Groups - Simply Explained
- Microsoft 365 Copilot Agents: Real Business Value with Steve Corey [MVP]
- Zero Trust AI Security with Microsoft Copilot and Azure – Mourtaza Fazlehoussen [MVP]
Discover more practical Microsoft conversations on M365 FM.
Apple Podcasts · Spotify · YouTube · YouTube Music
Host: Mirko Peters