 EN
 Deutsch
 Español
 Français
 Italiano
 Português
 Nederlands
 Polski
 Bahasa Indonesia
 Русский
 Українська
 العربية
 עברית
 हिन्दी
 日本語
 한국어
2026-07-18 · Season 3
Microsoft Graph Data Connect - Simply Explained
Show notes
Welcome to another episode of Knowledge Nuggets with Mirko Peters. In this episode, we're exploring Microsoft Graph Data Connect, Microsoft's enterprise-scale solution for extracting large volumes of Microsoft 365 data into Azure or Microsoft Fabric for analytics, reporting, machine learning, security investigations, and governance. While the regular Microsoft Graph API works well for real-time requests and smaller datasets, it becomes difficult to manage when organizations need to extract millions of records across SharePoint, Teams, Exchange, OneDrive, and other Microsoft 365 services. Graph Data Connect solves that scale problem through scheduled bulk data pipelines that avoid traditional API pagination and throttling. WHY MICROSOFT 365 DATA IS DIFFICULT TO EXTRACT Microsoft 365 generates enormous volumes of business activity every day. Emails, Teams messages, meetings, files, site activity, user interactions, and collaboration signals continuously accumulate across the tenant. The Microsoft Graph API provides access to this information through individual requests. This works well when an application needs a limited number of records in real time. However, large-scale analytics projects quickly encounter pagination, rate limits, HTTP 429 throttling responses, retry logic, and long processing times. Trying to analyze every SharePoint site, mailbox, or Teams interaction across a large organization using traditional API calls can take hours or days. Graph Data Connect was designed specifically for these scenarios, allowing organizations to extract Microsoft 365 datasets in bulk rather than requesting records individually. WHAT IS MICROSOFT GRAPH DATA CONNECT? Microsoft Graph Data Connect is a secure bulk data extraction service for Microsoft 365. It allows organizations to define a dataset, select a destination, and run a scheduled pipeline that transfers large volumes of Microsoft 365 data directly into an analytics environment. The extracted data can include information from services such as:
- Microsoft Teams
- SharePoint Online
- OneDrive
- Exchange Online
- Microsoft 365 Groups
- User and collaboration activity
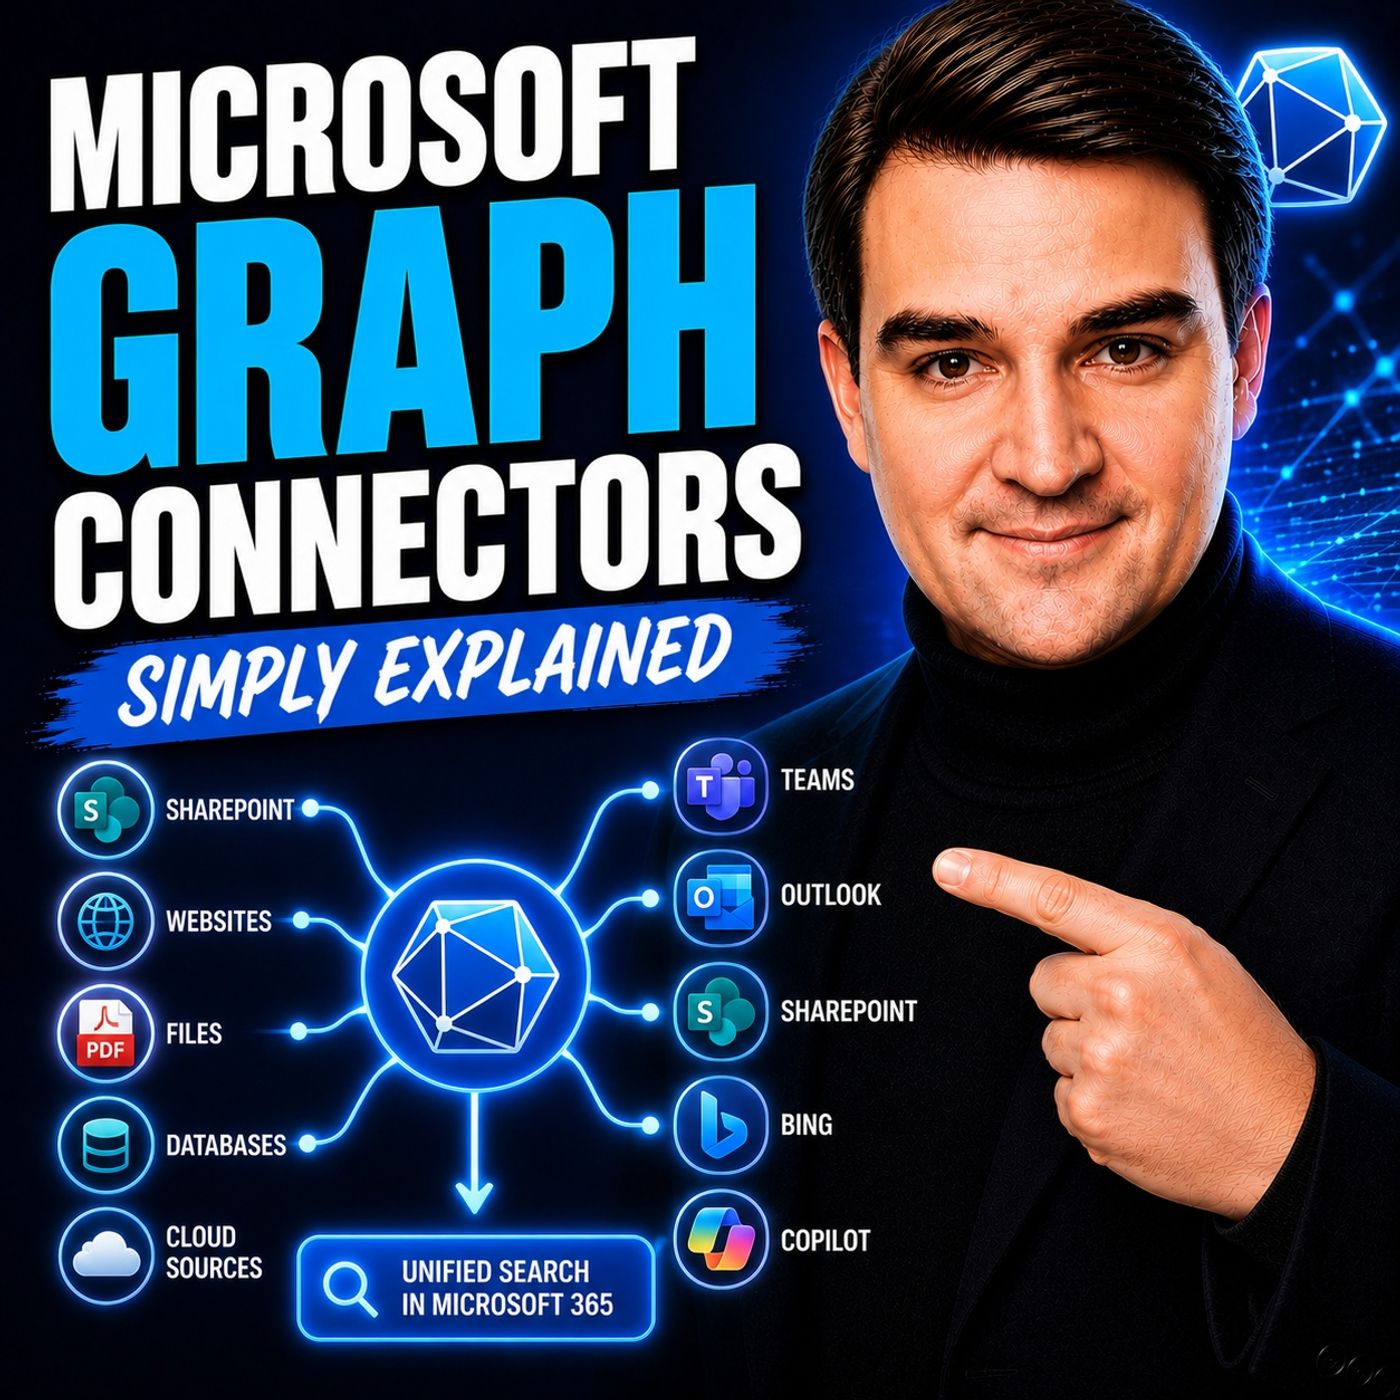
The data is delivered in analytics-friendly formats such as Delta Parquet, making it ready for SQL queries, Power BI reports, machine learning models, and large-scale processing inside Microsoft Fabric or Azure. Graph Data Connect is not a replacement for the Microsoft Graph API. The Graph API is designed for real-time application requests, while Data Connect is optimized for scheduled bulk extraction across an entire Microsoft 365 tenant. GRAPH API, GRAPH CONNECTORS, AND DATA CONNECT These three Microsoft Graph technologies solve very different problems. The Microsoft Graph API retrieves Microsoft 365 information through real-time request-and-response calls. It is ideal for applications that need current information about individual users, messages, files, or calendar events. Microsoft Graph Connectors bring external information into Microsoft 365 so it can appear in Microsoft Search and Copilot. Their purpose is ingestion and indexing. Microsoft Graph Data Connect moves Microsoft 365 data out of the tenant and into an external analytics environment. Its purpose is large-scale extraction. A simple way to remember the difference is:
- Graph API: request individual Microsoft 365 records
- Graph Connectors: bring external data into Microsoft 365
- Graph Data Connect: export Microsoft 365 data for analytics
Understanding this distinction helps organizations select the correct tool instead of forcing a real-time API or automation platform to perform bulk analytics workloads. SECURITY, PRIVACY, AND GOVERNANCE Because Graph Data Connect can process sensitive organizational information, its security model includes strict governance controls. Every application requires explicit administrator approval before it can access Microsoft 365 datasets. Administrators can control which datasets and properties are available, ensuring that applications receive only the information required for the approved business scenario. Data is encrypted during transfer, and organizations can use customer-managed encryption keys through Azure Key Vault for additional control. Identity obfuscation can replace personal identifiers with non-reversible tokens, allowing organizations to analyze collaboration patterns and behavioral trends without directly exposing individual identities. Every extraction is logged, creating an audit trail showing which application accessed the data, who approved it, which datasets were transferred, and when the pipeline ran. These controls make Graph Data Connect suitable for regulated industries and privacy-sensitive analytics scenarios. WHERE THE DATA CAN GO Graph Data Connect integrates with modern Azure and Microsoft analytics platforms. Organizations can deliver extracted data into:
- Microsoft Fabric Lakehouses
- Azure Data Lake Storage
- Azure Blob Storage
- Azure Synapse Analytics
- Azure Data Factory pipelines
- Custom analytics platforms through additional processing pipelines
Microsoft Fabric provides one of the most accessible destinations because the extracted data arrives in Delta Parquet format and can immediately be analyzed using SQL, notebooks, Power BI, or machine learning tools. Once the data has been extracted, it can also be combined with information from CRM, ERP, HR, security, and operational systems to create a broader view of organizational performance. REAL-WORLD USE CASES Microsoft Graph Data Connect supports a wide range of enterprise analytics scenarios. Security analytics can detect unusual account behavior, suspicious file activity, abnormal downloads, or unexpected access patterns. Collaboration analytics can examine how teams communicate, which departments work together, and where organizational bottlenecks exist. Content governance can identify stale SharePoint files, duplicate documents, abandoned sites, excessive permissions, and sensitive information. Employee experience analytics can combine Microsoft 365 collaboration signals with HR information while protecting individual identities. Copilot readiness assessments can help organizations understand where information is stored, how permissions are configured, and whether sensitive content could be exposed before deploying Microsoft 365 Copilot. These use cases require large datasets that would be difficult or impractical to retrieve through standard Graph API requests. HOW TO SET UP GRAPH DATA CONNECT A typical Graph Data Connect implementation involves several steps. First, Graph Data Connect must be enabled in the Microsoft 365 Admin Center. Administrators then select which datasets should be available. Next, an application registration is created in Microsoft Entra ID to provide the extraction pipeline with a secure identity. A Graph Data Connect application is then configured and linked to the app registration. Administrators select the approved datasets, properties, and destination. The application must pass an explicit Microsoft 365 administrator approval process before it can access organizational information. Finally, a data pipeline is created in Microsoft Fabric or Azure Data Factory. The pipeline selects the Microsoft 365 dataset, applies filters, defines the destination, and schedules the extraction. Once the preparation stage is complete, the data is delivered in structured files that can be analyzed using Power BI, SQL, notebooks, or machine learning tools. LIMITATIONS AND CONSIDERATIONS Graph Data Connect is designed for scheduled analytics rather than real-time applications. Pipeline runs include preparation time before data begins transferring, which means the service is better suited to nightly, weekly, or periodic analytics jobs than live dashboards. Not every Microsoft 365 property is available through every dataset, so organizations should confirm dataset coverage before designing a solution. Each application requires administrative approval, and changes to requested datasets or properties may require additional consent. Graph Data Connect also uses consumption-based pricing, meaning larger tenants and broader datasets can generate substantial processing costs. Testing with a limited dataset before scaling to the entire tenant is therefore recommended. The platform also requires knowledge of data pipelines, storage formats, identity management, and governance. It is intended primarily for data engineering and enterprise analytics teams rather than simple citizen-development workflows. Become a supporter of this podcast: https://www.spreaker.com/podcast/m365-fm-microsoft-365-azure-cloud-power-platform-ai--6704921/support.
Apple Podcasts · Spotify · YouTube · YouTube Music · Deezer
Host: Mirko Peters
Guests
Related articles
Transcript
Read the full transcript
Today's topic is something most people haven't heard of, but it's one of the most powerful tools for pulling Microsoft 365 data out at scale. It's called Microsoft Graph Data Connecting. Here's the thing. You've probably tried grabbing data from SharePoint or Teams with the regular Graph API. It works fine for a few items, but when you need millions of records, throttling and pagination hit you hard. You get rate limits, HTTP 429 errors, and you end up spending more time managing retreats than actually getting work done. Graph Data Connect lets you skip all that. One single request can move terabytes of data into Azure or Microsoft fabric, no pagination, no throttling. By the end of this episode, you'll know exactly what it is, how it's different from the regular Graph APIs and when to use it. The scale problem with M365 data. So let's break down why regular API calls just don't cut it when you're doing big analytics. Every day Microsoft 365 generates billions of interactions. Email, send, Teams messages posted, files uploaded, meetings scheduled. That's data sitting inside your tenant. If you want to analyze it, say, to understand collaboration patterns across departments, you need to get it out. That's where the trouble starts. The standard Graph API is built for real time access. You ask for a user's messages and it gives you the last 20. Ask for the next 20 you page in it. If you ask too fast, you get throttled with HTTP 429 errors and you have to back off, wait and try again. For small scale, that works fine. But imagine you want to analyze every sharepoint site in a 10,000 user company, even with batching it would take hours or days and you'd be fighting rate limits the whole way. If you need to do this regularly, it's simply not sustainable. This is why Graph Data Connect exists. It's not a replacement for the Graph API. It's a completely different tool for a different job. The Graph API handles a real time access to small amounts of data while Data Connect is built for bulk extraction at massive scale. What Graph Data Connect actually is? So what is Graph Data Connect? Let's clear up a common confusion first. Microsoft Graph is the gateway to all Microsoft 365 data. It covers users, messages, files, calendar, teams, and security signals. It's the single endpoint for everything, but there are three different ways to interact with that data and people often mix them up. First up is the Graph API. That's the real time request response model. You ask for a single user's mailbox and you get it back instantly. It's great for building apps and handling small queries, but it's not built for scale. Then we have Graph Connectors. These bring external data into Microsoft 365 for search and co-pilot. It's ingestion.extraction. You're pulling data in, not pulling it out. And finally, there's Graph Data Connect. This is bulk extraction. It pulls massive data sets out of Microsoft 365 into your own analytics environment. That's the one we're talking about today. Think of it this way. Using the Graph API is like asking a librarian for one book at a time. You walk up to the desk, ask for a book, they hand it to you, and then you walk back and ask for another. It works, but it's slow. Graph Data Connect is like saying, I want a copy of every book in this section and having them delivered to your office on a pallet. One request, one delivery, everything you need. So how does it actually work? You create a scheduled pipeline where you define what data you want, SharePoint sites, Teams, chats, Exchange mailboxes, and set a destination like an Azure storage account or a fabric lake house. Then Microsoft delivers that data as parking files directly into your storage, no pagination, no throttling, just one copy job, and it's done. The data arrives in Delta Parquet format, which is efficient and ready for analysis. You can query it with SQL, build Power BI reports, or run machine learning models. All of that comes from a single extraction pipeline. So that's the core idea. Graph Data Connect is for when you need to analyze your entire M365 data state, not just a small slice. Next, we'll talk about the security model that keeps your sensitive data safe, the security and governance layer. Now, you might be thinking, can I just dump everyone's emails into a storage account and do whatever I want? The answer is no, and here's why that's actually a good thing. Because Graph Data Connect handles sensitive data like emails, Teams, messages, and files, its security model is faster after than the regular Graph API. And that's by design, you don't want to tool this powerful without proper guardrails. First, it requires explicit admin consent. An administrator must approve each application and define exactly which data sets it can access. And I mean exactly. You can scope it down to the property level, want only site URLs, but not site owners, you can set that. Want only message timestamps, but not message content, you can set that to this is way more granular than standard Graph API permissions, which are usually all or nothing for a given resource type. Second, the data is encrypted in transit by default. Microsoft delivers it to your storage already encrypted, and if you want even more control, you can bring your own encryption keys through Azure Key Vault. Here's how it works. Your data gets encrypted with a key that only you hold. Microsoft stores the encrypted version of that key, but can't decrypt it. Only your application using your private key can unlock the data. This means even Microsoft can't read your data during delivery. Third, there's identity obfuscation. Real user IDs like email addresses and user principle names get replaced with non-reversible tokens. So you can still analyze trends, how many users access the file, or which department communicates most, but you can't tie that data back to a specific person. This is critical for privacy compliance, especially with regulations like GDPR. Fourth, every pipeline run is locked, creating a complete audit trail that shows who approved what, when data was extracted, which data sets were used, and how much data was transferred. If an auditor asks who accessed this data and why, you have the answer. This security layer is what makes data connect safe for regulated industries like healthcare, finance, and government. You get the analytics power without the compliance headache. The data never leaves your control, and every step is tracked. Where can the data go, sons? So once the data leaves Microsoft 365, where does it actually end up? Originally, graph data connect could only send data to Azure Synapse or Azure Data Lake Storage. That worked fine if you were a data engineer who lived in those tools. But if you were a business analyst or just starting out, it wasn't exactly friendly. Today that's changed. Data connect now works directly with Microsoft Fabric, and you can set a fabric lake house as your destination. The data shows up as Delta Park A files ready to analyze with no extra setup needed. If you're already using fabric, this is the simplest path, but you're not stuck with just fabric. You can also use Azure Data Factory Pipelines to manage the extraction, schedule it to run nightly, and your analytics environment always has fresh data. You can point it at Azure Blob Storage, Azure Data Lake, or any compatible destination. But here's the thing, you're not locked into one destination. Your options include Azure, Fabric, and even third-party platforms through custom pipelines. Once the data arrives, it's yours. You decide where it goes and what happens to it. That flexibility is what makes it valuable. You can combine M365 data with data from other systems, like your CRM, your ERP, your HR platform, and build one complete picture of your entire business. That's something you simply can't do with the regular Graph API alone. How it compares to other extraction tools. You might be thinking, can't I just use Power Automate or a custom script? Let's talk about when each tool works and when it doesn't. Power Automate is great for real-time, small-scale automation. You trigger a flow when a file is added, and it sends a notification. That works, but here's the thing. Power Automate handles kilobytes, not terabytes. It has no bulk extraction pattern, if you try to pull millions of records through a flow, it will time out, hit API limits, or just fail quietly. It's the wrong tool for this job. Custom Graph API scripts are fine for small data sets. You write a PowerShell script, loop through pages, and get your data. But pagination and throttling limits make it impractical for full-tenant analytics, because you'd need to manage retries, batching, and rate limits yourself. And if your script runs for hours and fails halfway through, good luck debugging that one. Azure Data Factory has over 90 connectors and is a solid choice for managing ETL pipelines. But ADF itself doesn't connect directly to M365 data at scale. It needs a source connector, and that's where data connect fills the gap. ADF becomes the manager, and data connect becomes the data source. Graph Data Connect is built specifically for bulk M365 data. One pipeline can extract millions of records. The trade-off is latency. Every pipeline run has about a 45 minute overhead before the data starts moving. So it's not for real-time dashboards. It's for scheduled, large-scale analytics that run nightly or weekly. Think of it this way. Power Automate is real-time, handled small data, and is low-code. The Graph API is real-time, handles medium data, and requires a developer. Graph Data Connect is scheduled, handles massive data, and requires admin consent. That's three different tools for three different jobs. If you need a real-time alert when a file changes, use Power Automate. If you need to analyze usage patterns across all your SharePoint sites every night, use Graph Data Connect. Don't try to make one tool do something it wasn't built for. Real-world use cases. So what does all this data actually let you do? Let me give you a few concrete examples. First up is security analytics. You can pull audit logs and activity data from Exchange and SharePoint, then run anomaly detection to spot compromised accounts or weird data access patterns. If an employee suddenly downloads thousands of files at 2 in the morning, you'd want to know about it. Data Connect gives you the raw data to build that kind of detection. Collaboration insights is another big one. By analyzing Teams messages and meeting data, you can see how Teams really work together. Which departments talk to each other most? Where are the bottlenecks in your workflow? You can answer questions like across functional Teams actually collaborating or just sitting in meetings without guessing. Then there's content management at scale. You can pull metadata from millions of SharePoint files, find stale content that hasn't been touched in years, identify duplicate files, eating up storage and flag documents with sensitive labels that shouldn't be there. That kind of data hygiene is impossible to do manually, but with Data Connect it's straightforward. Employee experience is a growing use case. Combine Viva Insights data with HR data to answer questions like, are Teams with frequent meetings more or less productive? The key is identity obfuscation. You can analyze patterns without exposing individual identities. So you get inside without the privacy risk and here's one that's becoming really important. Copilot readiness. Before you roll out Microsoft Copilot, you need to understand your data estate. Where does your data live? How is it organized? What permissions are in place? Data Connect can give you that inventory. You can see which sites have excessive permissions, which files are orphaned and where sensitive data might be exposed. Without that foundation, Copilot could surface things you'd rather it didn't. Here's a real example. The Polytechnic University of Milan used Data Connect to analyze employee sentiment at scale across thousands of users. They got objective granular data they couldn't have gotten any other way. No surveys, no bias, just real behavioral data from how people actually work. That's the power of this tool. A simple setup walkthrough. This might sound complicated, but the actual setup is surprisingly straightforward. Let me walk you through it. First, enable Graph Data Connect in the Microsoft 365 Admin Center. Go to org settings, find the Data Connect toggle, and turn it on. Then select which data sets you want to make available. SharePoint, OneDrive, Exchange, Teams. You can always add more later. Second, create an app registration in Microsoft Entra ID. This is your applications identity. Think of it like an ID badge for the pipeline. You'll need to note the app ID and generate a client secret. Keep that secret somewhere safe. You'll need it when you set up the connection. Third, create a Graph Data Connect application in the Azure portal. Link it to the app registration you just created, then choose your destination. For most beginners, a fabric lake house is the easiest option. No extra storage accounts to manage, no complex configuration. Just point and go. Fourth, this is the governance gate. Go back to the Microsoft 365 Admin Center and approve the application. And administrator reviews the requested data sets and permissions. What data will be accessed, which columns are included, and then gives consent. This step ensures nothing happens without explicit approval. Fifth, build a pipeline in fabric or Azure Data Factory. Use the copy activity with the Microsoft 365 source. Select your data set. For example, SharePoint sites basic. Configure a date filter if you only want recent data. Point it to your lake house. That's the bulk of the work done. Sixth, run the pipeline. Here's where you wait. There's about 45 minutes of initial preparation while Microsoft gets your data ready. After that, data streams in as Delta Park A files. And that's it. From there, you can query the data with SQL, build Power BI reports, or run machine learning models, all within fabric, limitations, and what to watch for. Before you run off to set this up, let me walk you through a few things to keep in mind. First, latency. That 45 minute overhead is real. So data connect is not for real time dashboards. If you need to see data updated every few minutes, this isn't your tool. It's designed for nightly or weekly analytics, so plan accordingly. Next, cross tenant access. You cannot pull data into a different Microsoft 365 tenant. The data stays inside your organizational boundary. If you're a consultant managing multiple tenants, you'll need separate pipelines for each one. Data set availability is another thing to watch. Not all M365 data is available through data connect. The basic data sets cover SharePoint, Exchange, Teams, and Groups. But some advanced properties may be missing. Check the documentation before you commit to a specific analysis. Now, costs. Data connect has consumption-based pricing. Your charge per object retrieved. For a small tenant, that's negligible. But for 100,000 user tenant with millions of files, it adds up fast. Budget accordingly and test with a small data set first. Approval process matters too. Every application needs explicit admin consent. And if you change the data set, so add new columns, you need to re-approved. Build that into your workflow so you're not caught off guard when a pipeline stops working. And one more thing, this isn't for citizen developers. Unlike power automate, data connect requires a data engineering mindset. You need to understand pipelines, storage formats like Parquet, and identity management. It's powerful, but it's not low-code. Bottom line. Graph data connect is a valuable tool for the right use case. Just know when to use it and when to reach for something simpler. So there you have it. Microsoft Graph Data Connect is the hidden pipeline that lets you extract M365 data at scale for real analytics. The key takeaway is simple. If you need to answer big picture questions about your organization, how people collaborate, where data lives, and what security risks exist, data connect is your tool. If you need real-time answers, use the Graph API or power automate. Different tools for different jobs. Here's what I'd suggest. Go to your Microsoft 365 admin center and check if Graph Data Connect is enabled. Even if you never use it knowing it's there and understanding how it works, puts a powerful tool in your back pocket. Next time, we'll explore how to combine this data with Microsoft Fabric for a complete analytics solution. If you enjoyed this episode, subscribe on your favorite podcast platform so you don't miss it.