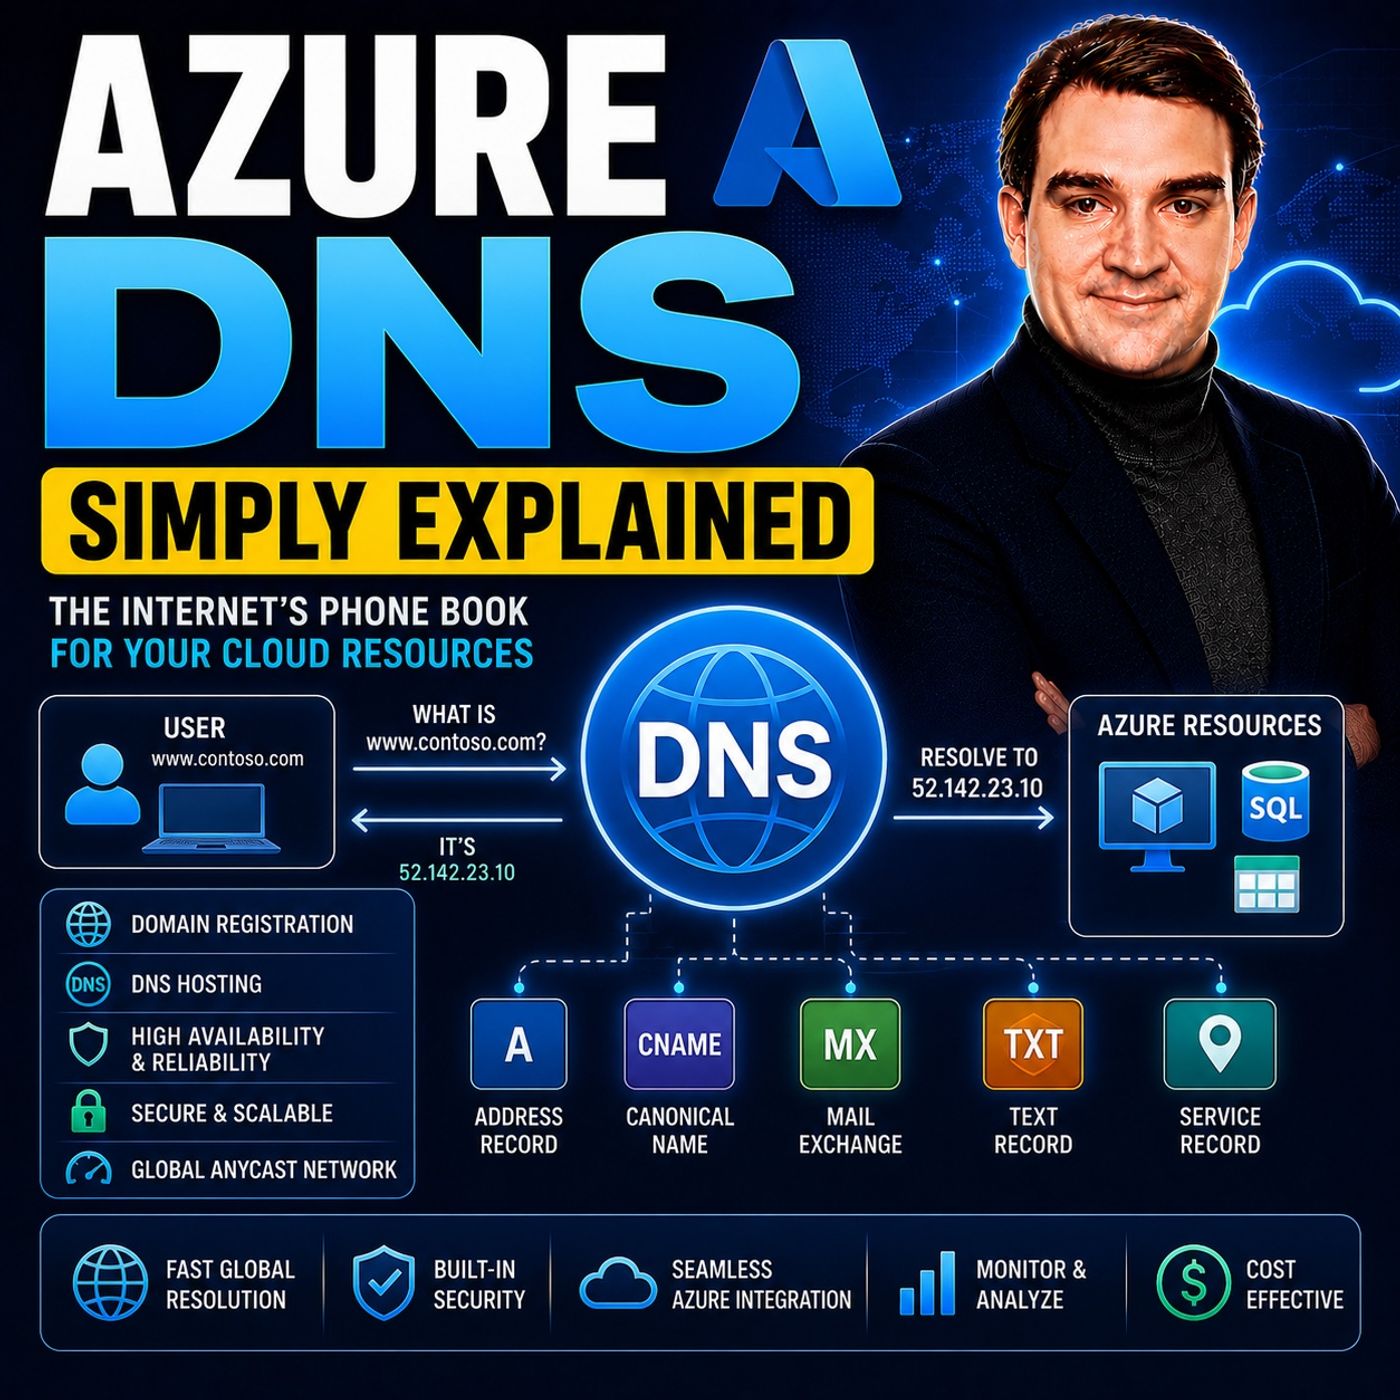
Mastering Azure DNS: Public vs. Private Zones Explained
Welcome to our deep dive into Azure DNS. In modern cloud architecture, getting your naming resolution right is just as important as configuring your firewalls or sizing your virtual machines. Whether you are launching a global e-commerce storefront or securing internal microservices across hybrid networks, mastering your Domain Name System configuration is vital. In this post, we will break down the critical differences between Azure public and private DNS zones, explore how the system works behind the scenes, and share best practices to help you optimize your cloud infrastructure.
For an audio breakdown of these concepts, be sure to check out the related podcast episode Azure DNS - Simply Explained.
Azure DNS Overview
What Is Azure DNS?
Azure DNS is a cloud-based Domain Name System (DNS) service provided by Microsoft. It allows you to host your DNS domains and manage DNS records easily. With Azure DNS, you can translate user-friendly domain names into IP addresses, enabling seamless communication between devices. This service eliminates the need for you to maintain your own DNS servers, making it a hassle-free solution for businesses and developers.
Azure DNS supports both public and private DNS zones. Public DNS zones are ideal for internet-facing domains, while private DNS zones cater to internal resources within Azure Virtual Networks. This flexibility allows you to manage your DNS needs effectively, whether for public websites or internal applications.
Importance of DNS
DNS plays a critical role in modern cloud infrastructure. It serves as the backbone for service discovery, application connectivity, and disaster recovery. Here are some key reasons why DNS is essential:
- Service Discovery: DNS helps applications find each other in a cloud environment. Without it, services would struggle to connect.
- Rapid Scalability: DNS enables quick adjustments to your infrastructure. You can scale your services up or down without downtime.
- Hybrid Cloud Strategies: DNS facilitates seamless integration between local and cloud resources. This integration is vital for maintaining operational consistency.
The consequences of DNS failures can be severe. When DNS goes down, businesses may face significant challenges. For instance, employees cannot access cloud applications, and customer-facing services become unreachable. This disruption can lead to financial losses, lost productivity, and reputational damage.
To illustrate the various purposes of Azure DNS in cloud networking environments, consider the following table:
| Service | Purpose |
|---|---|
| Azure Public DNS | Hosts DNS domains and allows management of DNS records using Azure credentials and tools. |
| Azure Private DNS | Manages and resolves domain names internally within virtual networks. |
| Azure DNS Private Resolver | Facilitates DNS queries between Azure DNS private zones and on-premises environments. |
| Azure Traffic Manager | Distributes traffic to public-facing applications across global Azure regions. |
How Azure DNS Works
DNS Resolution Process
When you use Azure DNS, the DNS resolution process involves several key steps. Here is how it works:
- Access Azure Portal: Start by logging into the Azure Portal. Navigate to create a DNS Zone.
- Create the DNS Zone: Provide a unique domain name. Select the appropriate subscription and resource group for your DNS zone.
- Add DNS Records: Open the DNS zone resource and add necessary DNS records, such as A Records and CNAME Records.
- Update Domain Registrar Settings: Obtain Azure DNS name servers. Update the NS records at your domain registrar to point to Azure.
- Verify Configuration: Use tools like MXToolbox or command-line utilities to verify DNS propagation and ensure everything is set up correctly.
This process ensures that your domain name translates into the correct IP address, allowing users to access your services seamlessly.
Integration with Azure Services
Azure DNS integrates smoothly with various Azure services, enhancing your cloud experience. Here are some ways it works with other Azure offerings:
- Azure DNS provides DNS resolution capabilities that improve communication between resources across different virtual networks.
- It supports private DNS zones for internal name resolution. This feature allows consistent hostname usage across peered networks, making it easier to manage your resources.
- Azure DNS integrates with Azure Traffic Manager, which helps with effective load balancing and disaster recovery. This integration ensures that your applications remain available and responsive, even during high traffic periods.
The global infrastructure of Azure DNS ensures low-latency DNS resolution for users worldwide. By utilizing a distributed network of DNS name servers, Azure DNS resolves queries closer to the user. This setup reduces latency and improves the overall user experience. A single Azure public DNS zone is served by name servers located in multiple Azure regions, ensuring that users receive DNS responses from the nearest Azure location by default.
Key Features of Azure DNS
Public and Private Zones
Azure DNS offers both public and private zones, catering to different needs. Public DNS zones allow you to host DNS records for domains accessible over the internet. This feature is essential for businesses that want to ensure their websites and services are reachable globally. In contrast, private DNS zones serve internal domains within Azure networks. This setup enhances security and simplifies communication between your Azure resources.
Here is a quick comparison of the two types of zones:
| Feature | Public DNS Zone | Private DNS Zone |
|---|---|---|
| Purpose | For public domains and global internet access | For private domains and internal communication within Azure networks |
| Accessibility | Accessible over the internet | Accessible only within Azure networks |
| Use Case | Hosting DNS records for public services | Hosting DNS records for internal services |
Security and Reliability
Security is a top priority for Azure DNS. The service implements several measures to protect against DNS attacks. For instance, the Azure DNS Security Policy allows you to filter and log DNS queries at the virtual network level. You can create rules to block name resolution for known malicious domains. This proactive approach helps safeguard your resources.
Additionally, Azure DNS continuously updates its threat intelligence feed. This ensures protection against newly detected malicious domains. You can monitor and block these domains while gaining visibility into DNS traffic through detailed logs. Here are some key security features:
- Smart protection against attacks that often start with a DNS query.
- Continuous updates to the threat intelligence feed.
- Monitoring and blocking of malicious domains with logging for visibility.
Reliability is another significant aspect of Azure DNS. The service operates on a globally distributed Anycast network, ensuring low-latency DNS resolution. This setup provides enterprise-grade resilience, allowing your applications to remain accessible even during high traffic periods.
Dynamic DNS Management
Dynamic DNS management in Azure DNS enhances operational efficiency for IT teams. Automation of DNS configurations minimizes human error, a common cause of outages. You can manage changes to DNS records through a review process, which enhances reliability. This feature is particularly useful when scaling your infrastructure.
Azure DNS also integrates seamlessly with infrastructure as code tools. This compatibility ensures consistent and auditable DNS management. Here are some benefits of dynamic DNS management:
- Automation reduces the risk of manual errors.
- Changes are reviewed for reliability.
- Integration with Azure services streamlines operations.
By leveraging these features, you can optimize your DNS management and improve the overall performance of your cloud applications.
Configuring Azure DNS
Setting Up DNS Zones
Setting up DNS zones in Azure DNS is straightforward. Follow these steps to create your DNS zone:
- Log into the Azure Portal: Start by accessing the Azure Portal with your credentials.
- Create a DNS Zone:
- Navigate to the "Create a resource" section.
- Search for "DNS Zone" and select it.
- Click on "Create."
- Fill in the Required Information:
- Choose your subscription.
- Select or create a resource group.
- Enter a unique name for your DNS zone, such as
example.com.
- Review and Create: After filling in the details, review your settings and click "Create" to finalize the DNS zone.
Once you complete these steps, your DNS zone will be ready for managing DNS records.
Managing DNS Records
Managing DNS records is essential for directing traffic to your resources. Azure DNS allows you to create various types of records, including A Records and CNAME Records.
A Records
A Records map a domain name to an IP address. Here is how to create an A Record in Azure DNS:
- Access Your DNS Zone: In the Azure Portal, navigate to your DNS zone.
- Add a Record Set:
- Click on "+ Record set."
- In the "Name" field, enter the subdomain or leave it blank for the root domain.
- Select "A" as the record type.
- Enter the IP address you want to associate with the domain.
- TTL Settings: Set the Time to Live (TTL) value, which determines how long the record is cached by DNS resolvers.
- Save the Record: Click "OK" to save your A Record.
By following these steps, you can effectively manage your A Records and ensure that users reach the correct IP addresses.
CNAME Records
CNAME Records allow you to alias one domain name to another. This is useful for pointing multiple domain names to a single resource. Here is how to create a CNAME Record:
- Access Your DNS Zone: Go to your DNS zone in the Azure Portal.
- Add a Record Set:
- Click on "+ Record set."
- Enter the subdomain name in the "Name" field.
- Choose "CNAME" as the record type.
- Enter the target domain name that you want to point to.
- TTL Settings: Set the TTL value for the CNAME Record.
- Save the Record: Click "OK" to save your CNAME Record.
Best Practices for Managing DNS Records
To ensure effective management of your DNS records, consider these best practices:
- Collect Private DNS zone requirements: Identify the specific DNS zone requirements for different Azure Manager services.
- Pre-Create private DNS zones: Set up all necessary private DNS zones in advance for better governance and management.
- Link VNET to private DNS zones and create conditional forward: Ensure proper linking of VNETs to the DNS zones for effective resolution.
By following these practices, you can enhance the governance and management of your Azure DNS setup.
Practical Applications of Azure DNS
Hosting Websites
Azure DNS plays a vital role in hosting websites. It provides a reliable and efficient way to manage your domain names. With Azure DNS, you can ensure that your website remains accessible to users around the globe. The service offers built-in redundancy, which enhances reliability. Here is a quick overview of how Azure DNS supports website hosting:
| Azure DNS Service | Type of Redundancy | Purpose |
|---|---|---|
| Azure DNS Private Zones | Built-in zone and geo redundancy | Internal name resolution |
| Azure DNS Public Zones | Built-in zone and geo redundancy | External name resolution |
| Azure DNS Private Resolver | Zone redundancy with self-healing | Hybrid name resolution between on-premises and cloud |
| Multiple Private Resolvers | Eliminates single point of failure | Resilient hybrid name resolution across regions |
This setup ensures that your website can handle high traffic without downtime. Azure DNS utilizes a global network of servers, ensuring high availability and performance.
Load Balancing
Load balancing is another critical application of Azure DNS. It helps distribute traffic across multiple endpoints, ensuring that no single server becomes overwhelmed. Azure DNS integrates with Azure Traffic Manager to provide global DNS load balancing. Here are some routing methods you can use:
- Performance routing for the lowest latency.
- Priority routing to direct traffic to a primary endpoint with backups.
- Weighted round-robin for distributing traffic based on assigned weights.
- Geography-based routing to direct traffic based on user location.
- Subnet-based routing for directing traffic based on user IP address range.
- Multi-value routing for returning multiple endpoints in a single DNS response.
These methods allow you to optimize your application’s performance and availability. By leveraging Azure DNS for load balancing, you can ensure that users experience minimal delays when accessing your services.
Internal Resource Management
Azure DNS also excels in managing internal resources within enterprise networks. It simplifies name resolution for Azure resources, enhancing communication between services. Here is how Azure DNS supports efficient internal resource management:
| Feature | Benefit |
|---|---|
| Manage DNS resolution in your virtual networks | Enhances internal resource management by ensuring efficient name resolution within Azure environments. |
| Enable name resolution between Azure and your on-premises resources | Facilitates seamless integration and communication between cloud and on-premises resources. |
| Enable autoregistration for VMs | Automates the registration of virtual machines, simplifying resource management. |
| Secure hybrid networking | Provides security for hybrid environments, ensuring safe communication between resources. |
| Monitor DNS metrics and alerts | Allows for proactive management and troubleshooting of DNS-related issues. |
By utilizing Azure DNS, you can streamline your internal operations and improve overall resource management. This capability is crucial for organizations that rely on both cloud and on-premises resources.
FAQ
What is Azure DNS?
Azure DNS is a fully managed Domain Name System service by Microsoft. It allows you to host DNS domains and manage DNS records easily, translating user-friendly domain names into IP addresses.
How do I create a DNS zone in Azure?
To create a DNS zone, log into the Azure Portal, navigate to "Create a resource," select "DNS Zone," and fill in the required information. Review your settings and click "Create."
Can I use Azure DNS for internal resources?
Yes, Azure DNS supports private DNS zones. These zones allow you to manage internal resources within Azure Virtual Networks securely and efficiently.
What types of DNS records can I manage?
You can manage various DNS records in Azure DNS, including A Records, CNAME Records, MX Records, and Alias Records. Each record type serves different purposes for directing traffic.
How does Azure DNS ensure security?
Azure DNS implements security measures like filtering and logging DNS queries. You can create rules to block known malicious domains, enhancing the protection of your resources.
What is the benefit of dynamic DNS management?
Dynamic DNS management automates DNS configurations, reducing human error. It allows for efficient scaling and integrates with infrastructure as code tools for consistent management.
How does Azure DNS improve website performance?
Azure DNS utilizes a global network of servers for low-latency DNS resolution. This setup ensures high availability and performance, allowing users to access your website quickly.
Can I monitor DNS performance in Azure?
Yes, Azure Monitor provides insights into DNS query volumes and operational health. You can track performance metrics and receive alerts for any issues, ensuring optimal DNS management.
🎧 Listen to this episode
Want a practical explanation of Azure DNS? This episode breaks down the topic in clear language and shows why it matters for Microsoft 365, Azure, Power Platform, security, AI, and modern work.
Listen to this episode if you want to:
- Understand the key concepts behind Azure DNS
- See how it fits into the wider Microsoft technology ecosystem
- Learn where it can create practical value for your organization
Discover more practical Microsoft conversations on M365 FM.
Last reviewed: July 2026.
Who Should Listen
This episode is for Microsoft 365 administrators, architects, IT leaders, and practitioners who need a practical understanding of Azure DNS before planning, implementing, or supporting it.
In summary, Azure DNS simplifies DNS management for businesses and developers. You can host both public and private DNS zones, ensuring your resources are accessible and secure. The service enhances reliability and security through its global infrastructure.
To optimize your cloud infrastructure, consider exploring advanced features of Azure DNS. For instance, use Azure DNS Private Resolvers to forward DNS queries between Azure and on-premises networks. Implementing DNS caching on-premises can also minimize query latency. By leveraging these features, you can enhance your organization's operational efficiency and performance.
Embrace Azure DNS today to streamline your DNS management and improve your cloud experience! For an even deeper dive, make sure to listen to our dedicated podcast discussion on Azure DNS - Simply Explained.

Microsoft MVP | Host of M365.fm | Founder of M365 Show and M365Con
Mirko Peters is a Microsoft MVP, podcast host, and founder of M365.fm, M365 Show, and M365Con. His work connects Microsoft practitioners through podcast interviews, livestreams, and community events.
At M365.fm, Mirko hosts conversations with Microsoft MVPs, product experts, architects, and community contributors. Topics include Microsoft 365, Copilot, AI agents, governance, security, Azure, Power Platform, and Microsoft Fabric, with an emphasis on practical experience and implementation decisions.
M365.fm is the podcast and learning platform. M365 Show brings experts together for livestreams, while M365Con provides an online conference setting for community learning.
Official website: Mirko Peters (https://www.mirkopeters.com/). Recognition: Mirko Peters — Microsoft MVP profile (https://mvp.microsoft.com/de-DE/mvp/profile/9b0ca797-db5a-493a-a845-8b9158046cf5). Connect on LinkedIn (https://www.linkedin.com/in/m365showpodcast/).