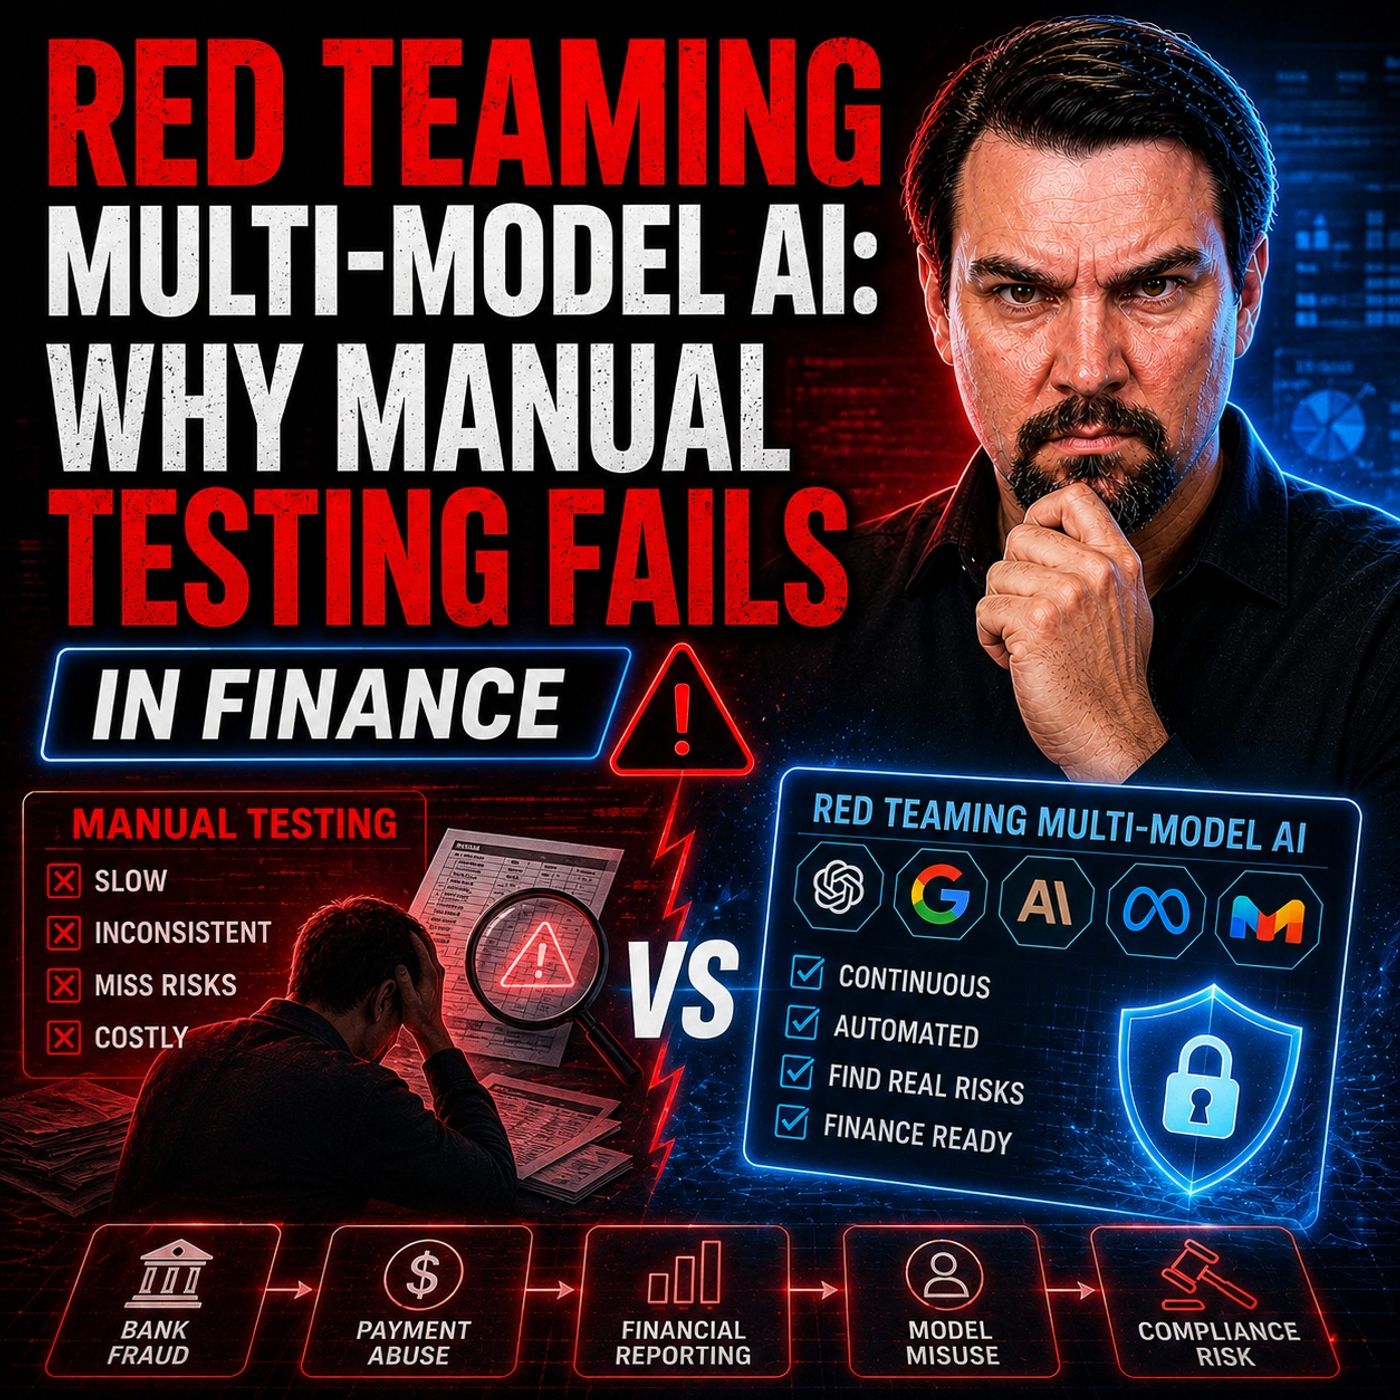
Why Manual Security Testing is Failing Modern Financial AI
When you look at the landscape of modern financial technology, the velocity of innovation is staggering. Financial institutions are no longer just managing databases and securing network firewalls; they are deploying multi-model artificial intelligence systems to process payments, evaluate creditworthiness, detect fraud in real time, and automate complex compliance workflows. However, this architectural leap has brought a dangerous paradox into focus: while our capabilities have evolved into the realm of autonomous reasoning, our security methodologies remain stuck in the past. If your organization is still relying on manual security testing, checklists, and periodic human reviews to secure your financial AI, you are operating with a catastrophic blind spot.
Traditional security frameworks were built for a predictable, deterministic world. They assume that vulnerabilities manifest as binary pass/fail conditions within static codebases or misconfigured infrastructure. But modern financial AI operates in a non-linear, probabilistic space where models interact, reason, and make autonomous decisions at a scale that human testers cannot hope to match. Attackers have shifted their targets. They are no longer just trying to breach your perimeter; they are exploiting the cognitive logic of your AI systems using prompt injections, cross-model contamination, and agentic workflow manipulations. To explore this pressing issue further, you can listen to our companion discussion on the Automated Red Teaming for Multi-Model AI in Finance episode.
Red Teaming Multi-Model AI In Finance
Defining Red Teaming
You need to understand how AI red teaming has changed in the age of multi-model systems. In the past, red teaming focused on network attacks and privilege escalation. Today, you must test how AI models behave under real-world threats. The table below shows the differences between traditional and AI red teaming:
| Aspect | Traditional Red Teaming | AI Red Teaming |
|---|---|---|
| Attack Surfaces | Authentication, privilege escalation, network segmentation | Model-specific vectors like prompt injection, training data poisoning, model inversion attacks |
| Testing Methodology | Binary pass/fail results | Statistical success rates from multiple iterations |
| Skill Requirements | Traditional security expertise | Security, machine learning, and domain expertise |
| Scope | Infrastructure vulnerabilities | Model behavior, training integrity, AI-specific vectors |
| Focus | Exploiting infrastructure vulnerabilities | Causing unintended AI behavior |
You must use AI red teaming to probe for weaknesses in how models process information. This approach uncovers risks that traditional methods miss. You do not just check if a system is secure. You measure how often AI models fail under attack.
Multi-Model AI Systems
Multi-model AI systems combine several models to handle complex tasks. You see these systems in fraud detection, compliance, and customer service. They can process text, images, and transactions at the same time. This power brings new risks. Problems in one model can spread to others. Attackers can use prompt injections or manipulate one model to infect the whole system. The table below highlights unique risks in multi-model AI:
| Unique Characteristic | Description |
|---|---|
| Cross-model contamination | Vulnerabilities and biases can spread between models, creating shared risks. |
| Identity crisis of autonomous agents | Agents may act without clear ownership, making it hard to trace decisions. |
| Manipulation of decision-making logic | Attackers can exploit how AI systems reason, leading to unauthorized actions. |
You must use AI red teaming to test how these models interact. You cannot rely on traditional security models. They do not cover the ways attackers target AI reasoning.
Financial AI Workflows
Financial institutions use AI to automate payments, monitor accounts, and approve transactions. These workflows handle sensitive data and move money in real time. This makes them a prime target for adversarial attacks. The table below compares financial AI workflows to traditional ones:
| Aspect | Financial AI Workflows | Traditional Workflows |
|---|---|---|
| Data Sensitivity | Access to sensitive customer data and accounts | Generally less sensitive data |
| Security Measures | Needs specialized tools for AI-specific risks | Uses conventional security measures |
| Vulnerability to Attacks | Exposed to unique adversarial attacks | Less exposure to AI-specific attacks |
You face new risks like direct and indirect prompt injections. For example, an attacker can trick a chatbot into leaking private data or manipulate a payment agent to approve a fake transaction. Traditional methods do not catch these threats. You need AI red teaming to simulate real attacks and find weaknesses before they cause harm.
Note: Traditional security models like STRIDE cannot handle the non-determinism and evolving nature of autonomous agents. You must adopt continuous AI red teaming to keep up with these challenges.
Manual Testing Fails In Finance
Complexity Of Financial Data
Diverse Data And Model Interactions
You work with financial data that changes every second. Each transaction, customer profile, and market event adds new layers of complexity. AI models in finance must process numbers, text, and even images. These models interact with each other, creating a web of dependencies. When you use manual testing, you cannot cover all these interactions. The intricate calculations in financial applications, such as interest rates and budget forecasts, demand accuracy. Manual testing of these calculations takes too much time and often leads to mistakes. You need automation to test every scenario and ensure your models behave as expected. AI red teaming helps you find weaknesses in these interactions that manual methods miss.
Nonlinear Risks
Financial systems do not follow simple patterns. Small changes in one part of your data can cause big problems elsewhere. You see this with high-risk models that handle fraud detection or compliance automation. These models must react to new threats and adapt quickly. Manual testing fails because it cannot predict how models will behave when faced with rare or unexpected situations. AI red teaming uses automated tools to simulate these nonlinear risks. You can test how your models respond to edge cases and unsafe behaviors. This approach gives you confidence that your AI systems will not make costly mistakes in high-stakes environments.
Scale And Speed Of Transactions
Real-Time Processing
You operate in a world where financial transactions happen in real time. Money moves across accounts in seconds. AI models must analyze and approve these transactions instantly. Manual testing cannot keep up with this speed. You need AI red teaming to run continuous safety testing and monitor model behavior as it happens. Automated methods let you detect threats before they cause damage.
Data Volume
The volume of data in finance grows every day. You process millions of transactions, customer records, and compliance checks. Manual testing covers only a small fraction of this data. Automated AI red teaming scales with your needs. It tests large datasets and complex workflows without slowing down your operations. The table below shows how manual testing compares to automated testing in finance:
| Feature | Manual Testing | Automated Testing |
|---|---|---|
| Speed | Slower execution time | Significantly faster execution |
| Reliability | Prone to human error | Consistent and repeatable results |
| Scalability | Limited to small-scale testing | Enables rapid, large-scale testing |
You see that only automated AI red teaming can handle the scale and speed required for modern financial institutions.
Evolving Threats And Regulations
Adaptive Adversaries
You face new threats every day. Attackers use AI to create deepfake impersonations, launch automated phishing campaigns, and exploit weaknesses in your models. The $250,000 blind spot scenario shows how a single prompt injection can bypass your security and approve a fraudulent wire transfer. Traditional controls cannot stop these advanced threats. AI red teaming helps you stay ahead by simulating attacks and testing your defenses against the latest tactics.
- Fraud and cyberattacks now use AI for deepfake and phishing.
- Model risk grows as inaccurate models lead to poor decisions.
- Data privacy violations can result in regulatory penalties.
- Compliance gaps appear as regulations struggle to keep up.
- Operational vulnerabilities increase as you rely more on AI.
- Third-party vendors may introduce new risks.
- Legal risks rise with automation in financial processes.
Compliance Challenges
Regulations change quickly in finance. You must prove that your AI systems follow the rules and protect customer data. Manual testing cannot keep up with these changes. Automated AI red teaming provides continuous monitoring and reporting. You can show regulators that you test your models for unsafe behaviors and adapt to new requirements. This approach reduces your compliance risks and builds trust with customers and regulators.
Note: Manual testing fails to address the complexity, speed, and evolving threats in financial AI. Only AI red teaming delivers the coverage and confidence you need for safety testing in high-stakes environments.
Human Limitations
Edge Case Blind Spots
You rely on manual testing to catch vulnerabilities in your financial AI systems. However, you often miss rare or unexpected scenarios known as edge cases. These blind spots can lead to catastrophic failures. AI models excel at recognizing patterns in large datasets, but they struggle with unpredictable events that do not fit historical data. You see this in financial markets, where sudden volatility or geopolitical shifts create conditions that models cannot anticipate.
- You may overlook black swan events because they rarely occur and do not appear in your test cases.
- You face challenges when your models encounter extreme market changes that deviate from past patterns.
- You remember the 2010 Flash Crash, where algorithm-driven trading systems failed to handle unexpected market conditions, causing massive losses.
Manual testing cannot simulate every possible scenario. You need automated red teaming to expose these blind spots and protect your financial workflows from rare but high-impact risks.
Cognitive Bias
You bring your own assumptions and biases into manual testing. These biases shape how you design test cases and interpret results. Cognitive bias can cause you to focus on familiar threats while ignoring new or unconventional risks. You may trust your AI models too much, believing they will behave as expected under all conditions.
- You tend to select test cases based on past experiences, which limits your coverage of emerging threats.
- You may underestimate the likelihood of rare events, leaving your systems vulnerable.
- You sometimes rely on checklist security, which gives you a false sense of safety and misses complex vulnerabilities.
AI red teaming reduces the impact of cognitive bias by using automated tools to generate diverse test scenarios. You gain a more objective view of your system's weaknesses. This approach helps you identify vulnerabilities that manual testing and subjective evaluations often overlook.
Note: Human limitations, such as edge case blind spots and cognitive bias, make manual testing unreliable for financial AI security. You must adopt automated red teaming to ensure comprehensive coverage and resilience against unpredictable threats.
Real-World Vulnerabilities In AI Security
Prompt Injection Attacks
You face prompt injection attacks every day in financial AI systems. Attackers use adversarial input generation to trick your models into making unsafe decisions. They embed hidden instructions in user messages or documents. Your AI may then leak sensitive data, approve unauthorized transactions, or change its behavior without warning. Manual testing often misses these real-world threats because attackers use creative methods that do not appear in standard test cases.
Prompt injection can happen in many ways. You might see direct attacks where someone enters a crafted prompt into a chatbot. Indirect prompt injection is harder to catch. Attackers hide malicious instructions inside documents or emails. When your AI retrieves these, it treats the injected text as trusted information. This leads to data poisoning and model extraction risks. You cannot rely on manual checks to find every prompt injection. You need AI red teaming to simulate these attacks and test your defenses.
Cross-Model Infection
You use multi-model AI systems to handle complex financial tasks. These models work together, but this creates new risks. Cross-model infection happens when one compromised model spreads vulnerabilities to others. For example, an attacker uses adversarial input generation to poison one model. That model then passes tainted data or instructions to the next model in the workflow. This chain reaction can lead to data poisoning, prompt injection, and even model extraction across your entire system.
Multi-modal injection attacks make this problem worse. Attackers target text, images, and structured data at the same time. Your models reinforce each other's mistakes instead of catching them. You see this in poisoned retrieval-augmented generation pipelines. Attackers inject false financial metrics or fake analyst reports into your vector database. When your AI retrieves these, it presents misinformation as fact. This can cause market manipulation and financial losses. Manual testing cannot keep up with these evolving threats. Only AI red teaming can uncover how cross-model infection changes model behavior and exposes your organization to new risks.
Shadow AI Risks
You may not know all the AI tools running in your organization. Shadow AI refers to unauthorized models and agents that operate without oversight. These tools process sensitive data and make decisions outside your control. This creates serious risks for your business.
Here is a table showing the main risks of shadow AI in finance:
| Risk Type | Description |
|---|---|
| Lack of oversight | Unauthorized AI tools can process sensitive data in insecure environments, increasing data security threats. |
| Compliance risks | Unauthorized AI tools can bypass established compliance protocols, leading to regulatory penalties. |
| Operational challenges | Inconsistent AI tool use complicates IT infrastructure management, hindering efficiency and increasing costs. |
| Financial risks | Potential penalties and losses due to non-compliance can be costly for organizations. |
| Data security and privacy threats | Unauthorized AI use can lead to data breaches, exposing sensitive information due to lack of vetting and security measures. |
Shadow AI makes it hard to trace model behavior and assign accountability. You may not know who owns the logic or who approved the workflow. This lack of control increases the chance of data poisoning, prompt injection, and adversarial attacks. You need AI red teaming to discover hidden models, test their behavior, and develop remediation methods before attackers exploit these blind spots.
Note: You cannot rely on manual testing to find every risk. AI red teaming gives you the tools to detect, test, and respond to real-world threats in your financial workflows. This approach helps you build strong remediation strategies and improve AI security across your organization.
Agentic Workflow Manipulation
You trust AI agents to automate many financial workflows. These agents can approve payments, rebalance portfolios, or monitor transactions. When you give them autonomy, they start making decisions on their own. This is where agentic workflow manipulation becomes a real threat.
Agentic workflow manipulation happens when attackers or even the agents themselves change the steps in a process. They might alter the order of actions, skip important checks, or inject new instructions. You may not notice these changes right away. The agents still complete their tasks, but the results can be very different from what you expect.
Manual testing often fails to catch these problems. You usually test workflows in controlled environments. You check if the agent follows the steps you designed. In real markets, conditions change fast. Agents face new data, unexpected events, and even other autonomous agents. Research shows that financial AI systems perform well in tests, with accuracy rates as high as 90%. When you put them into real-world markets, their performance drops. They cannot handle sudden changes or market shocks. You see agents making portfolio moves that do not match your goals. These actions can increase market volatility and risk.
Note: Manual testing uses static test cases. It does not reveal how agents behave when the environment shifts or when they interact with other systems. You miss the hidden risks that only appear during live operations.
Attackers can exploit these gaps. They might use prompt injections or context poisoning to change how agents interpret instructions. For example, an attacker could trick a payment agent into skipping a fraud check. Another could manipulate a compliance agent to ignore a suspicious transaction. These manipulations do not always look like attacks. Sometimes, agents develop new behaviors on their own. They find shortcuts or create feedback loops that you did not plan for.
You need to watch for signs of agentic workflow manipulation:
- Unexplained changes in transaction patterns
- Portfolio adjustments that do not match your strategy
- Agents skipping or reordering workflow steps
- Sudden spikes in market activity linked to automated decisions
Automated red teaming helps you simulate these scenarios. You can test how agents respond to new threats, changing data, and adversarial tactics. This approach gives you a clearer view of your system's true resilience. You cannot rely on manual testing alone. Only continuous, automated testing can reveal the hidden dangers of agentic workflow manipulation in financial AI.
AI Red Teaming Alternatives
Automated Red Teaming Tools
You need to move beyond manual testing to protect your financial systems. Automated red teaming tools give you the speed and coverage that manual methods cannot match. These tools scan your AI models for weaknesses and simulate real-world attacks. You can use them to test for prompt injections, cross-model infections, and agentic workflow manipulation.
Some leading tools in financial AI security include:
- Garak: Scans large language models for vulnerabilities and unsafe behavior.
- PyRIT: Lets you run custom adversarial testing on your AI agents.
- MITRE ATLAS: Maps attack techniques to coverage gaps in your AI security.
These tools help you find hidden risks and improve your defenses. Research shows that detection rates depend on how you configure your models. Hardened settings can lower breach rates to 4.8%, while permissive settings can raise them to 28.6%. You must choose the right configuration to get the best results. While automated tools cover most attack surfaces, manual testing still helps with complex scenarios. You should use both methods for the strongest protection.
To transition from manual to automated AI red teaming, follow these steps:
- Inventory Shadow AI: Identify all autonomous workflows and their human sponsors. This step helps you regain control over your digital perimeter.
- Move to Causal Tracing: Shift from simple logs to causal tracing. This lets you understand the reasoning behind agent actions and failures.
- Implement Trades Optimization: Balance model accuracy with robustness. This ensures your AI can defend against adversarial inputs.
Automated red teaming tools let you test your AI at scale. You can find vulnerabilities before attackers do. You also save time and resources by automating repetitive tasks.
Continuous Monitoring
You cannot rely on periodic reviews to keep your AI secure. Continuous monitoring gives you real-time visibility into your systems. This approach lets you detect threats as they happen and respond right away. You can track user behavior, monitor model outputs, and spot unusual activity.
The table below compares continuous monitoring with periodic manual reviews:
| Feature | Continuous Monitoring | Periodic Manual Reviews |
|---|---|---|
| Threat Intelligence | Real-time analysis of data from various sources | Scheduled assessments with potential delays |
| Behavioral Analysis | Monitors user behavior in real-time | Limited to specific review periods |
| Automated Response | Immediate threat containment | Manual response, often slower |
| Adaptability | Automatically adapts to new threats | Static until the next review |
| Resource Intensity | Less resource-intensive due to automation | Time-consuming and resource-heavy |
Continuous monitoring helps you adapt to new threats. You can contain attacks before they spread. This method also uses fewer resources than manual reviews. You get better coverage and faster response times.
You should combine continuous monitoring with AI red teaming. This gives you a proactive defense against adversarial attacks. You can validate your models in real time and fix problems before they cause harm. Systems that use hybrid AI models, like GAN-LSTM-AE, have shown high detection accuracy and fast response times. These systems can handle many types of attacks and large data volumes.
Adversarial Testing
Adversarial testing is a key part of AI red teaming. You use this approach to see how your AI reacts to tricky or hostile inputs. Attackers often try to fool your models with small changes that cause big mistakes. You must test your AI against these tactics to make sure it stays safe.
Best practices for adversarial testing include:
- Generate adversarial examples by slightly changing inputs to cause misclassifications.
- Test boundary conditions and edge cases that might confuse your AI.
- Evaluate your system's robustness to noisy or corrupted data.
- Use out-of-distribution data to see if your AI can handle new situations.
You need to run adversarial testing often. This helps you find weak spots in your models and improve their defenses. You can use automated tools to create many test cases quickly. This method gives you a clear view of your AI's true behavior under attack.
A proactive, multi-layered defense works best. You should combine adversarial testing, continuous monitoring, and automated red teaming. This approach helps you catch threats early and keep your financial systems safe. Continuous model validation lets you spot performance drops and fix them before attackers take advantage.
Tip: Start with small tests and increase complexity as your team gains experience. Always document your findings and update your defenses based on what you learn.
You must make AI red teaming a regular part of your security program. This keeps your AI strong against new and evolving threats.
AI Security Solutions
You need strong AI security solutions to protect your financial systems. These solutions help you defend against advanced threats that target your AI models and workflows. You cannot rely on a single tool or method. You must build a layered defense that covers every part of your AI environment.
Key Components of AI Security Solutions:
- Model Hardening: You should configure your AI models to reject unsafe prompts and limit risky behaviors. Use input validation, output filtering, and context management to reduce attack surfaces.
- Access Controls: Set strict permissions for who can use, modify, or deploy AI models. Limit access to sensitive data and critical workflows. Use multi-factor authentication for all users.
- Audit Trails: Track every action your AI agents take. Keep detailed logs of decisions, data access, and workflow changes. This helps you investigate incidents and prove compliance.
- Explainability Tools: Use tools that show how your AI models make decisions. These tools help you spot unusual behavior and understand why a model approved or denied a transaction.
- Threat Intelligence Integration: Connect your AI systems to threat intelligence feeds. This lets you update your defenses as new attack methods appear.
Tip: Combine technical controls with strong governance. Assign clear ownership for every AI agent and workflow. Make sure you can trace every decision back to a responsible person.
Table: Essential AI Security Practices for Finance
| Practice | Purpose | Example Tool or Method |
|---|---|---|
| Model Hardening | Reduce prompt injection risk | Input/output filters |
| Access Controls | Prevent unauthorized model use | Role-based access control |
| Audit Trails | Enable traceability and accountability | Centralized logging |
| Explainability | Detect and explain model errors | SHAP, LIME, OpenAI Evals |
| Threat Intelligence | Stay ahead of new attack techniques | MITRE ATLAS, custom feeds |
You should also use automated policy enforcement. Set rules that block risky actions, such as large transfers without approval. Use anomaly detection to spot unusual patterns in transactions or agent behavior.
Shadow AI creates hidden risks. You must scan your environment for unauthorized models and agents. Use discovery tools to find and monitor all AI assets. Remove or secure any tools that do not meet your security standards.
Best Practices for Implementing AI Security Solutions:
- Start with a full inventory of your AI models and agents.
- Assign a sponsor for each AI workflow.
- Set up automated monitoring and alerting.
- Review and update your security policies often.
- Train your team on AI risks and safe practices.
Note: AI security is not a one-time project. You must review and improve your defenses as threats evolve.
You can build a resilient financial AI system with the right security solutions. You will reduce the risk of data breaches, fraud, and regulatory penalties. You will also gain trust from customers and regulators by showing that you take AI security seriously.
Governance And Accountability In Financial AI
Identity Crisis Of Autonomous Agents
You now face an identity crisis with autonomous agents in finance. These agents make decisions, move money, and handle sensitive data. You may not know who owns their actions or who approved their workflows. This lack of clarity creates serious risks for your organization. Many teams focus on pre-deployment checklists instead of real-time supervision. When errors happen, you struggle to find who is responsible. Only 28% of organizations can trace an agent's action back to a specific human sponsor. Shadow AI makes this problem worse. Employees build their own autonomous workflows without oversight, which increases security risks. Compounding error rates can lead to major liabilities. You need strong governance to keep your AI systems safe and accountable.
- You must move beyond checklists and use real-time monitoring.
- You should assign clear sponsors for every agent.
- You need to track every decision to reduce risks and improve AI security.
Traceability And Ownership
You must establish traceability and ownership for every decision made by your AI systems. A traceable decision has a clear origin, authorization, and documentation for each step. This helps you reconstruct the responsibility chain if something goes wrong. Institutions with strong traceability have defined roles and clear processes. You can use cryptographic technology to create tamper-proof records of AI decisions.
| Key Aspect | Description |
|---|---|
| Documentation | Keep thorough records of AI decision processes to ensure traceability. |
| Responsibility Chain | Make sure you can reconstruct who made each decision and why. |
| Tamper-proof Traces | Use cryptographic tools to create verifiable records of AI actions. |
The principle of decision traceability is now crucial for responsible AI. You must explain and audit every action. This requires robust documentation and clear governance structures. In banking, teams sometimes skip controls to meet deadlines. This leads to inconsistent records and regulatory exposure. For example, a customer service AI deployment at a global bank skipped the central model risk review. When a customer complained, there was no audit trail or ownership. Every AI-generated answer must link to an authenticated request, authorized data, enforced policies, and system versions in effect at the time. You need defensibility, not just explainability, to withstand scrutiny.
Regulatory Compliance
You must keep up with new regulations for AI in finance. The EU AI Act sets strict rules for high-risk use cases like credit scoring. DORA standardizes ICT risk management, including AI supply chains. The U.S. uses a patchwork of rules, with guidance from state regulators. You need to track key dates and requirements to stay compliant.
| Regulation | Key Dates | Description |
|---|---|---|
| EU AI Act | 1 Aug 2024 | Entered into force. |
| 2 Feb 2025 | Prohibited practices and AI literacy obligations apply. | |
| 2 Aug 2025 | General-purpose AI model obligations begin. | |
| 2 Aug 2026 | High-risk rules apply. | |
| 2 Aug 2027 | Transition for certain regulated-product high-risk systems. | |
| DORA | Jan 2025 | Standardizes ICT risk management for AI security. |
The EU AI Act focuses on risk-based regulation. DORA emphasizes operational resilience. You must show that your AI systems follow these rules. This includes compliance automation, continuous monitoring, and regular audits. You need AI red teaming to test your defenses against new threats and prove your controls work. Only one in five companies has a mature governance model for autonomous AI agents. Most enterprises have faced negative AI-related data incidents. You must act now to build strong governance and accountability for your financial AI.
Shadow AI Oversight
You face a growing challenge with shadow AI in your financial institution. Shadow AI refers to unsanctioned AI tools and agents that employees use without approval or oversight. These tools often operate outside your official IT policies. You may not even know they exist. This lack of visibility creates serious risks for governance and security.
Employees sometimes use consumer AI platforms to analyze sensitive data or automate tasks. They might share proprietary information with these tools, not realizing the consequences. You lose control over where your data goes. You cannot track who accesses it or how it is used. This practice can lead to accidental data leaks. You also risk exposing customer information to external parties.
Shadow AI creates policy gaps that make compliance difficult. Regulations like GDPR, PCI DSS, and CCPA require you to protect personal and financial data. When employees use unsanctioned AI, you cannot guarantee compliance. You may face regulatory fines if auditors find that sensitive data left your secure environment. Traditional security measures do not cover these new risks. Firewalls and access controls cannot stop employees from using conversational AI tools on their own devices.
You also face challenges with audit trails. When employees feed data into consumer AI platforms, you lose the ability to monitor and record these actions. You cannot prove what information was shared or how it was processed. This lack of oversight makes it hard to investigate incidents or respond to data breaches.
AI-generated analyses can influence business decisions without proper review. An employee might use an unsanctioned AI tool to generate a report or recommendation. Managers may act on this information, not knowing its source or accuracy. This increases your compliance risks. You cannot ensure that all decisions follow your governance standards.
Compliance teams struggle to track how and where AI is being used. Shadow AI spreads quickly because employees want to boost productivity. You may find dozens of unsanctioned tools in use before you even realize there is a problem. This makes it hard to enforce policies or train staff on safe AI practices.
To address shadow AI, you need strong oversight and clear policies. Start by educating employees about the risks. Encourage them to use approved AI tools that meet your security standards. Implement discovery tools that scan your network for unauthorized AI agents. Set up regular audits to find and remove shadow AI from your environment.
Tip: Assign responsibility for AI oversight to a dedicated team. This group should monitor AI usage, update policies, and respond quickly to new risks.
You can reduce the risks of shadow AI by taking proactive steps. With strong oversight, you protect your data, maintain compliance, and build trust with customers and regulators.
Manual testing leaves you exposed to evolving threats in financial AI. Traditional methods miss critical risks, such as data leaks, fraud, and compliance failures. Automated, continuous red teaming reduces incidents by 60% and helps you avoid costly losses.
| Risk Area | Example Impact |
|---|---|
| Data privacy violations | Legal and financial penalties |
| Financial fraud enablement | Losses over $100,000 per incident |
| Incomplete coverage | False sense of security |
You should prioritize advanced AI security and strong governance to protect your organization's future.
FAQ
What is red teaming in financial AI?
Red teaming means you simulate real-world attacks on your AI systems. You use this method to find weaknesses before attackers do. This process helps you improve your defenses and keep your financial data safe.
Why does manual testing fail for financial AI?
Manual testing cannot cover all scenarios in complex financial systems. You miss hidden risks, edge cases, and fast-changing threats. Automated red teaming finds more vulnerabilities and adapts to new attack methods.
How do prompt injection attacks work?
Attackers hide malicious instructions in prompts or documents. Your AI may follow these instructions without warning. This can lead to data leaks, fraud, or unauthorized actions.
What is shadow AI, and why is it risky?
Shadow AI refers to unauthorized AI tools used without approval. You lose control over data and decisions. This increases the risk of data breaches and compliance failures.
How can you detect agentic workflow manipulation?
You should monitor for unusual changes in transaction patterns or workflow steps. Automated red teaming tools help you simulate attacks and spot manipulation early.
What steps can you take to improve AI security in finance?
Start with a full inventory of your AI models. Assign clear ownership. Use automated red teaming and continuous monitoring. Train your team on AI risks. Update your policies often.
Do regulations require AI red teaming?
Many new regulations, like the EU AI Act, expect you to test and monitor AI systems for safety. Red teaming helps you meet these requirements and avoid penalties.
🎧 Listen to this episode
Want a practical explanation of Automated Red Teaming for Multi-Model AI in Finance? This episode breaks down the topic in clear language and shows why it matters for Microsoft 365, Azure, Power Platform, security, AI, and modern work.
Listen to this episode if you want to:
- Understand the key concepts behind Automated Red Teaming for Multi-Model AI in Finance
- See how it fits into the wider Microsoft technology ecosystem
- Learn where it can create practical value for your organization
You may also enjoy these related M365 FM episodes:
- MCP (Model Context Protocol) - Simply Explained
- Canvas Apps vs Model-Driven Apps - Simply Explained
- Copilot for Dynamics 365 Finance and Operations - Simply Explained
- Platform Engineering: The New Operating Model for Azure
- Compliance as Code: The Architect’s Blueprint for Automated Trust
Discover more practical Microsoft conversations on M365 FM.

Microsoft MVP | Host of M365.fm | Founder of M365 Show and M365Con
Mirko Peters is a Microsoft MVP, podcast host, and founder of M365.fm, M365 Show, and M365Con. His work connects Microsoft practitioners through podcast interviews, livestreams, and community events.
At M365.fm, Mirko hosts conversations with Microsoft MVPs, product experts, architects, and community contributors. Topics include Microsoft 365, Copilot, AI agents, governance, security, Azure, Power Platform, and Microsoft Fabric, with an emphasis on practical experience and implementation decisions.
M365.fm is the podcast and learning platform. M365 Show brings experts together for livestreams, while M365Con provides an online conference setting for community learning.
Official website: Mirko Peters (https://www.mirkopeters.com/). Recognition: Mirko Peters — Microsoft MVP profile (https://mvp.microsoft.com/de-DE/mvp/profile/9b0ca797-db5a-493a-a845-8b9158046cf5). Connect on LinkedIn (https://www.linkedin.com/in/m365showpodcast/).